Writing
Series
All posts
- Social engineering in the logs · Part 1
What an MFA prompt actually proves.
Seven sign-in methods, what each one attests, and how each one gets beaten.
· 7 min read
- MITRE ATT&CK · Blog
The MITRE ATT&CK most people are learning was retired in October 2025.
What v18 and v19 changed, and how to read the framework now.
· 5 min read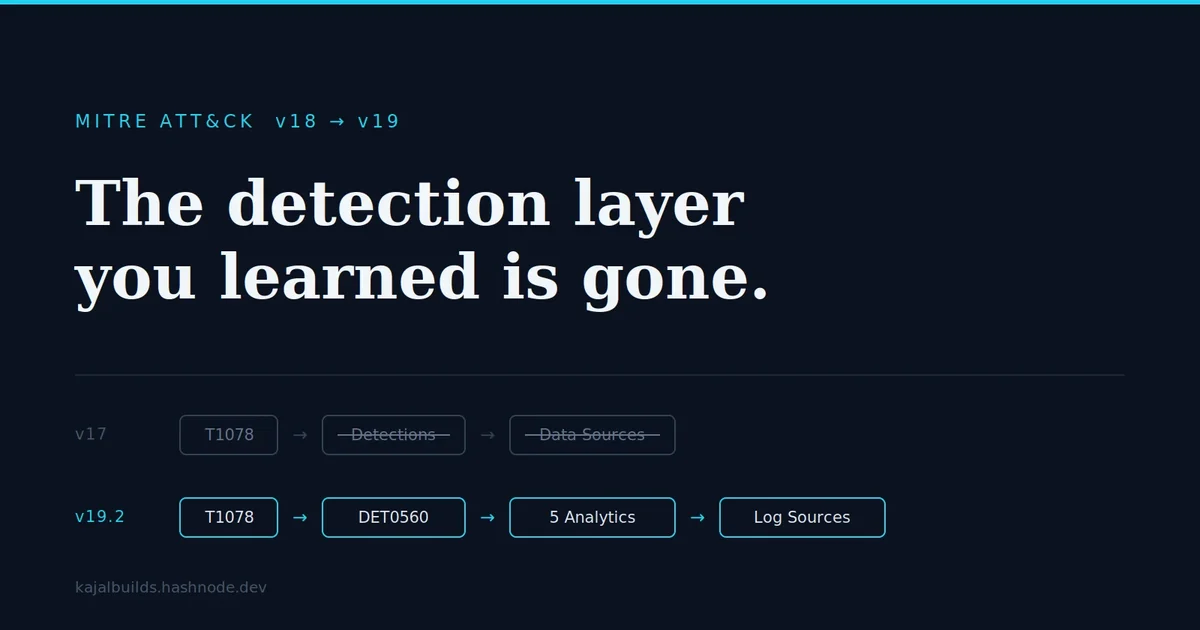
- Identity and Entra ID · Blog
Anatomy of an identity compromise
A login-only intrusion, step by step, and where the detection actually lives.
· 10 min read
- Detection engineering · Blog
What your logs can't see
Nine common sources and the gaps they carry by design.
· 7 min read
- AI security · Blog
FortiBleed had around twenty people. JadePuffer had an agent. The way in was identical.
A coverage audit of my own Sentinel detections.
· 12 min read
- Building a Sentinel detection lab · Part 8
Building a Sentinel Detection Lab, Part 8: Watching for Agents, Not Just Attackers
The same process-lineage technique, pointed at a different actor: not a human attacker, an AI agent.
· 3 min read
- Building a Sentinel detection lab · Part 7
Building a Sentinel Detection Lab, Part 7: The Detection That Taught Me My Own Telemetry's Blind Spot
Where AI tooling talks to once it's running, and the most useful failure in the lab so far.
· 3 min read
- Building a Sentinel detection lab · Part 6
Building a Sentinel Detection Lab, Part 6: Shadow AI and the Detection That's Honest About What It Hasn't Proven Yet
AI tooling showing up on endpoints with nobody in IT knowing it's there.
· 3 min read
- Incident response · Essay
Humans Aren't the Weakest Link
The line that excuses broken process, and what it costs dwell time.
· 5 min read
- Building a Sentinel detection lab · Part 5
Building a Sentinel Detection Lab, Part 5: MFA Registration, a Missing License, and the First Detection That Talks Back
Attackers registering their own MFA methods to keep access after a password reset, and the first detection that talks back.
· 7 min read
- Building a Sentinel detection lab · Part 4
Building a Sentinel Detection Lab, Part 4: Catching Reconnaissance, and the Case-Sensitivity Bug That Made It Look Broken
The first detection in the lab that looks for a pattern of behavior, and the case-sensitivity bug that made it look broken.
· 5 min read
- Building a Sentinel detection lab · Part 3
Building a Sentinel Detection Lab, Part 3: My Detection Flagged Legitimate Windows Behavior. Here's How I Tuned It Without Going Blind
Registry persistence, a textbook false positive, and the single most important lesson in detection engineering.
· 2 min read
- Building a Sentinel detection lab · Part 2
Building a Sentinel Detection Lab, Part 2: Suspicious PowerShell, and Why Some Detections Need No Threshold
Hunting malicious PowerShell with Sysmon, and the difference between volume detections and signature detections.
· 3 min read
- Building a Sentinel detection lab · Part 1
Building a Sentinel Detection Lab, Part 1: Catching Brute Force (and the Bug That Flagged the Wrong Account)
Writing my first detection, and the parsing bug that taught me more than the detection itself.
· 5 min read